WARNING--Time4Popcorn's Abandoned Updater Ran as Root on Up to 350,000 Macs and Took Unsigned Code From Expired Domains, Eye Security Switched It Off on Two Million Machines, and the Fix Is to Delete the App and PT.updd
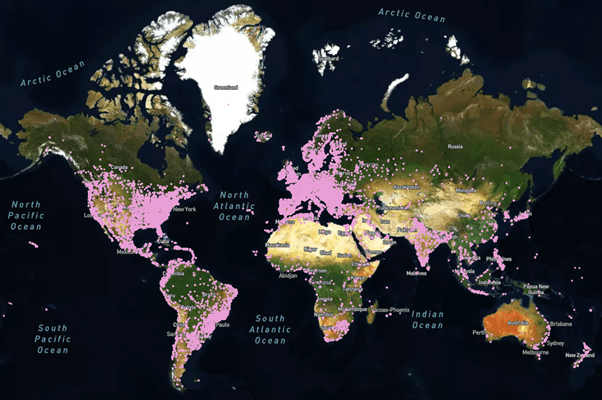
An abandoned copy of Popcorn Time left a background updater on every Mac that ever installed it, running as root from boot and ready to install whatever came back from web domains nobody owned any more. Eye Security's report, published October 22 by Niels Teusink, puts the count at 250,000 to 350,000 Macs and 2.5 to 3 million Windows PCs, and says Eye used the hole itself, from November 2025 to March 2026, to switch the updater off on more than two million machines. MacRumors' report brought it to Mac readers on October 29. If Popcorn Time was ever on your Mac, the app and its helper should go now.
The updater ran as root and asked no questions
The app is Time4Popcorn, the fork that carried the Popcorn Time name after the original BitTorrent movie client shut down in 2014. Eye's June 11 advisory puts the Mac build's privileged helper, PT.updd, in /Library/PrivilegedHelperTools, with a launch daemon in /Library/LaunchDaemons that starts it at every boot. In Eye's words, "On macOS, things were pretty much the same. We could push an update that would execute as root." The checker polled its update domains over plain HTTP with no code signing, so anyone who registered one of the expired domains could answer with a program of their choosing. Eye found it in a threat hunt when a Windows PC kept calling popcorntimeupd.xyz, a domain no one had renewed; once Eye registered it, requests came at about 50 a second. The CVE record for CVE-2026-30612, published August 27, rates it 9.8 of 10 and names Time4Popcorn for macOS up to version 6.2.1.17. Eye first thought it was seeing 1.7 million Macs; its best guess is 250,000 to 350,000, because the Mac build's hardware ID shifts with the hostname and with MAC address randomization, so one Mac looked like several. Our 2007 warning on the RSPlug trojan described a cron file that kept putting its bogus DNS addresses back.
Eye pushed its own update, then handed the domains to Shadowserver
With no vendor left to patch it, Eye registered 15 of the abandoned domains and, from November 2025, answered the checker with an update of its own. On the Mac it runs one command, launchctl unload -w /Library/LaunchDaemons/PT.updd.plist, and BleepingComputer's report says the payload "collected no host data or telemetry, and deleted no files on the users' computers." More than a million machines took it by December 2025 and over two million by March; on March 1, 2026, requests were down 98 percent. Eleven antivirus vendors flagged Eye's fix as malware within a week. Eye writes that "there was no vendor to fix this and no patch on the way: if we didn't act, nobody would." In late March it transferred the 15 domains to the Shadowserver Foundation, and SecurityWeek's report says the nonprofit still holds them as sinkholes.
What to do on your Mac
Eye's advice to anyone still running the app is to uninstall it: "If you're still using Popcorn Time, we think it's time to move on." The app itself, Eye says, "is built on a Chrome engine from 2014, with the sandbox disabled," and loads JavaScript over HTTP from domains that were abandoned too. Our steps:
- Drag Popcorn Time or Time4Popcorn from the Applications folder to the Trash.
- Open System Settings, then General, then Login Items & Extensions, and under App Background Activity look for a Popcorn Time or PT.updd item and switch it off. Apple's Login Items page says that setting lets apps run tasks "when the app isn't open, such as checking for software updates."
- In Terminal, run ls /Library/PrivilegedHelperTools/PT.updd /Library/LaunchDaemons/PT.updd.plist. If either file is there, Eye's own command, sudo launchctl unload -w /Library/LaunchDaemons/PT.updd.plist, stops the daemon, and sudo rm on each of the two files removes them. Malwarebytes' write-up gives the same two paths.
If Eye's update already reached your Mac, the daemon is unloaded but both files and the app remain. Eye's report says the Android build could not be fixed this way at all, because its updater is part of the app. We have not had the app on our Macs and have not run the steps.
Then and now
On October 30, 2003, we passed along @Stake's security warnings for Mac OS X 10.2 with a raised eyebrow, because the firm had just parted with the chief technologist who co-wrote a report calling reliance on Microsoft a security threat, and we told readers to upgrade to Panther regardless. Twenty-three years on, a firm found a Mac hole with no vendor left to warn, fixed it on two million machines it did not own, and then gave the domains away. We would rather no researcher had to make that choice, but we are glad this one did. [Macs Only!]
Sources
- Eye Security, “Operation IXIM: Preventing a botnet of millions of Popcorn Time users - Eye Research” accessed Oct 30, 2026
Niels Teusink, October 22, 2026: "Between November 2025 and March 2026, Eye Research actively disabled the vulnerable update mechanism used by the popular download client Popcorn Time (Time4Popcorn)"; "Popcorn Time is a BitTorrent client that allows users to view movies downloaded from the internet"; Time4Popcorn a closed-source fork after the original shut down in 2014; an Updater.exe on a client's system trying to reach the unregistered popcorntimeupd.xyz, registered by Eye, then about 50 requests per second; updates over HTTP with no code signing; "On macOS, things were pretty much the same. We could push an update that would execute as root"; the Mac update runs launchctl unload -w /Library/LaunchDaemons/PT.updd.plist; PT.updd "usually under '/Library/PrivilegedHelperTools/PT.updd'"; 2.5 to 3 million Windows systems; "Where we initially thought there were about 1.7M macOS hosts, this number is probably a lot lower. Our best guess would be 250-350k," because of hostname changes and MAC address randomization; "After about a month, in December 2025, we had already deployed an update to more than a million systems"; "On March 1, 2026, we were still sending about 5000 updates per day, which amounts to a 98% reduction"; "over 2 million update downloads"; "A week later 11 different vendors were detecting our update as malicious"; "With millions of systems affected and the software long abandoned, there was no vendor to fix this and no patch on the way: if we didn't act, nobody would"; "In late March, we transferred the 15 domains we owned to The Shadowserver Foundation"; "The application is built on a Chrome engine from 2014, with the sandbox disabled"; JavaScript loaded over HTTP from abandoned domains; "If you're still using Popcorn Time, we think it's time to move on"; no updates were deployed to Android because "the updater is part of the main application on Android so it can't be independently disabled"; the page's world map of affected systems, wp-content/uploads/image-82.png; accessed October 30, 2026.
- Eye Security, “CVE-2026-30612: A vulnerability in Time4Popcorn (PopcornTime) - Eye Research” accessed Oct 30, 2026
June 11, 2026: the Windows, Mac and Android builds of Time4Popcorn have an update mechanism that connects over an insecure channel; on Windows and macOS updates run silently as NT AUTHORITY\SYSTEM or root; the macOS helper is /Library/PrivilegedHelperTools/PT.updd, started at boot by /Library/LaunchDaemons/PT.updd.plist; on Android the updater is part of the app and the user is prompted to install the APK; the software is abandoned and the update infrastructure is sinkholed by The Shadowserver Foundation; accessed October 30, 2026.
- CVE, “CVE-2026-30612 - CVE” accessed Oct 30, 2026
The CVE record, read through the CVE Services API (cveawg.mitre.org/api/cve/CVE-2026-30612) because the page renders in the browser: "An issue in Time4 Popcorn for Windows <= 6.2.1.18 and Time4Popcorn for MacOS <= 6.2.1.17 and Time4Popcorn for Android <= 3.5.0.173 allows a remote attacker to execute arbitrary code via the updater.exe for windows, PT.updd on MacOS components"; published 2026-08-27 by MITRE; CVSS 3.1 base score 9.8, critical; CWE-494; accessed October 30, 2026.
- MacRumors, “Old 'Popcorn Time' App Left Hundreds of Thousands of Macs at Risk - MacRumors” accessed Oct 30, 2026
Tim Hardwick, Thursday October 29, 2026, 10:12 am PDT: Eye Research estimates 250,000 to 350,000 Macs; the Time4Popcorn update checker ran at every start with full permission to change anything on the Mac, even after the app was uninstalled; the developers abandoned the project and the addresses expired; the researchers disabled the checker on more than a million Macs and Windows PCs and transferred the addresses to the Shadowserver Foundation; the advice is to uninstall Time4Popcorn; accessed October 30, 2026.
- BleepingComputer, “Abandoned Popcorn Time app exposed millions of device to RCE attacks - BleepingComputer” accessed Oct 30, 2026
Bill Toulas, October 23, 2026: CVE-2026-30612; Time4Popcorn, a fork of the BitTorrent client, used unencrypted HTTP for updates without signature verification; up to 3 million Windows and 350,000 macOS connections observed; between November 2025 and March 2026 Eye Security used the mechanism to deploy code that disabled the updater; the payload "collected no host data or telemetry, and deleted no files on the users' computers"; 2 million update downloads; a 98 percent drop by March 1, 2026; domains passed to The Shadowserver Foundation; accessed October 30, 2026.
- SecurityWeek, “Dead Popcorn Time Updater Put Millions of Computers at Risk of Takeover - SecurityWeek” accessed Oct 30, 2026
Ionut Arghire, October 27, 2026: Time4Popcorn, an abandoned fork of the original Popcorn Time BitTorrent client; 2.5 to 3 million Windows devices and 250,000 to 350,000 macOS devices; Eye Security registered 15 abandoned domains and pushed a disabling update from November 2025; about 2 million systems patched by March 2026, a 98 percent reduction in requests; The Shadowserver Foundation took over the domains in late March and keeps them sinkholed; Eye recommends uninstalling the app; accessed October 30, 2026.
- Malwarebytes, “Popcorn Time's forgotten updater left millions of devices exposed to hijacking - Malwarebytes” accessed Oct 30, 2026
Pieter Arntz, October 26, 2026: the vulnerable macOS component is /Library/PrivilegedHelperTools/PT.updd with a launch daemon at /Library/LaunchDaemons/PT.updd.plist; Mac users should check their installed applications for Popcorn Time or Time4Popcorn, remove the old application entirely since no vendor update exists, and confirm the background updater is no longer running; accessed October 30, 2026.
- Apple Support, “Change Login Items & Extensions settings on Mac - Apple Support” accessed Oct 30, 2026
The macOS 27 Golden Gate user guide page: Apple menu, System Settings, General, Login Items & Extensions; the App Background Activity setting lets apps "perform tasks when the app isn't open, such as checking for software updates or syncing data" (the body quotes the clause up to "software updates"); accessed October 30, 2026.
Saw something? Send a tip or a correction
The archive ran on reader tips. What did you see, where, and do you want the credit? Something wrong on this page? Say so and it gets fixed.